Oh no... your WordPress website is hacked. Don't panic. Below you'll find how to spot a hack, what to do now and how to prevent the next one.
How does this happen?
The biggest mistake? People build their WordPress website and forget about it. No updates. No maintenance. They pick passwords like "password123" or keep the username "admin". They install plugins from unreliable sources, or keep outdated ones full of security holes. Even worse? Some use pirated themes and plugins. And without security monitoring, nobody notices the hack.
How do you spot a hacked website?
We help you with that. Every night, we check all websites in your web hosting account for malware. Did we find any? Then we email you, and the Security tab of your plan shows a red number. There you also see which files are suspicious and when the attacker last changed files. Read how the Security tab works.
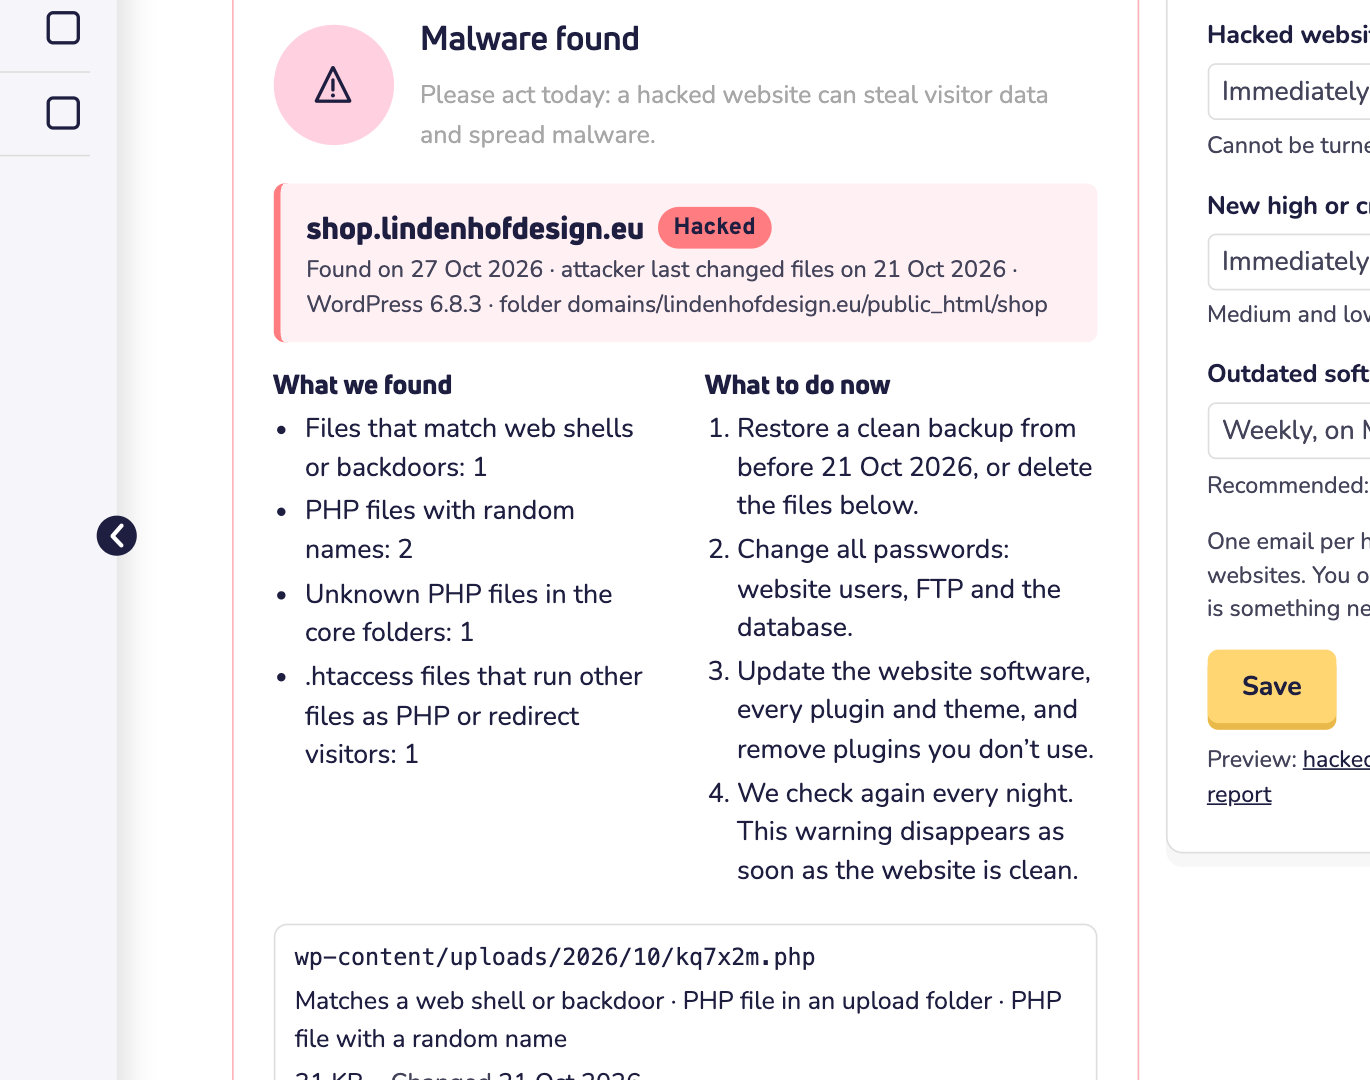
Other warning signs:
- Your website loads really slowly or crashes often.
- You get strange error messages.
- You see content you didn't create.
- You see strange code in your website's source code.
- Your website redirects to weird websites.
- Google warns visitors about your website.
- You're locked out of your own admin area.
Your website is hacked. What now?
Act the same day. A hacked website can steal your visitors' data, show spam or spread malware. You have two options.
Option 1: start fresh. Build your website again from scratch, and take security very seriously this time. This is the safest way. Reset your web hosting account first, so no hidden backdoor stays behind. Read what resetting a web hosting account does.
Option 2: clean it up. Restore a clean backup from before the date the attacker last changed files. Or delete the suspicious files. Read how to create and restore backups in Softaculous.
But here's the challenge: cleaning up a hacked website is very difficult. You need to find out how the attacker got in, and which files they changed. You never know which backdoors they left behind. Some companies specialize in cleaning up WordPress websites. Wordfence has a helpful guide too: How to clean a hacked WordPress site using Wordfence.
Whichever option you choose, also do this:
- Change all passwords: of your WordPress users, FTP and the database.
- Update WordPress and every plugin and theme. Remove what you don't use.
- Check the Security tab the next morning. Is the website clean? Then the warning disappears.
What not to do
When panic sets in, people make bad choices. Don't be one of them:
- Don't ignore it and hope it goes away. It won't. It gets worse if you do nothing.
- Don't pay ransoms. You're funding criminals. And they probably won't even fix your website.
How do you prevent a hack?
Prevention is better than cure. Here's what you need to do:
- Only install plugins from trusted sources, and keep them updated.
- Same goes for themes. Stick to well-maintained ones.
- Remove plugins and themes you don't use. Old plugins are security risks.
- Use strong passwords. Really strong ones.
- Keep WordPress itself updated. Always run the latest version.
- Turn on automatic updates for your plugins. Then most holes are closed before anyone can use them.
- Hide wp-admin from strangers and limit login attempts. That stops brute force attacks in their tracks. A security plugin does both. We recommend Wordfence. And actually follow its recommendations.
- Use two-factor authentication. Add that extra layer of protection.
- Keep an eye on the Security tab and its emails. Fix security holes and outdated plugins as soon as you see them.
Several websites? Spread the risk
Here's something important. Do you have several websites in one web hosting account, and one of them gets hacked? Then the attacker can reach all of them.
So consider spreading your websites over several web hosting accounts at Site.eu. We recommend this anyway. Spreading your websites over several servers also gives you the best redundancy.
Don't lose hope
Getting hacked feels terrible. We know. But thousands of WordPress websites get cleaned up every day. Yours can be one of them. Take website security seriously, especially with an open source system like WordPress. Then your website will be stronger than ever.